Category

Technical

25 articles

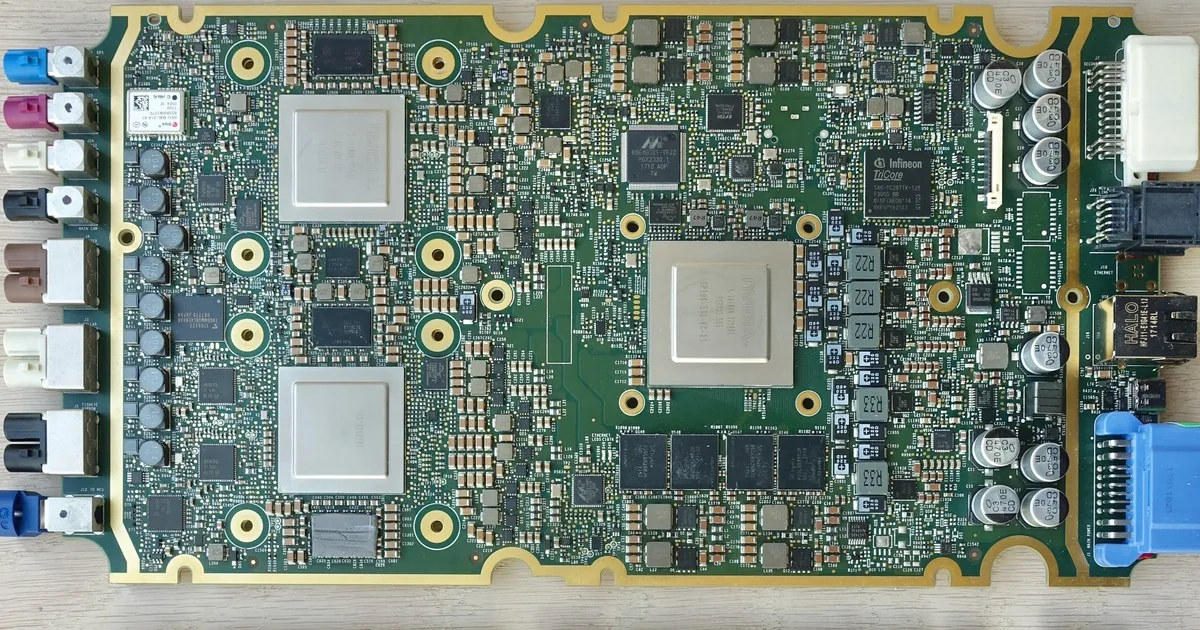
An automotive driver-assistance controller board with two identical processor packages side by side, next to a larger processor, memory, power components and a row of connectors, all on one PCB.

The Core Concept of Dependent Failure Analysis in ISO 26262

Two redundant channels are not automatically independent. What a dependent failure is, the difference between common cause and cascading failures, the coupling factors that tie elements together, and why ISO 26262 asks for DFA.

7 min
An engineer at a desk writing an AUTOSAR-style CAN driver in C for an ECU, with a cross-compiler build finishing with zero errors and a laptop showing ECU software domains and CAN traffic.

Software in ISO 26262: A Fault With No Failure Rate

Software has no failure rate, so ISO 26262 cannot count it. What the standard asks for instead, why software is both the safety net for hardware faults and a source of its own, and why Part 6 converges on the software architecture.

7 min
Close-up photograph of a populated circuit board with integrated circuits, resistors and capacitors under blue and orange lighting.

Hardware Element Evaluation: What Does the Evidence Prove?

A familiar component can face a different safety requirement in a new design. Explore what hardware element evaluation establishes, where its evidence stops, and why integration still matters.

3 min
Driver's view down a wet motorway. Heavy spray from the traffic ahead hangs over the carriageway in a low backlit sun, and the painted lane markings fade out well before the cars do.

The Automotive Safety Standards Map: Beyond ISO 26262

A modern car can cause the same accident four different ways. Only one of them is a malfunction. Lane centering steers into the next lane. Same severity, same exposure, same controllability. One hazard. Now ask why. A solder joint opened. Or the camera worked perfectly and lost the markings in low sun. Or someone forged a steering frame on the bus. Or the model met a road marking that was never in its training data. ISO 26262 owns the first one, and it says so itself. The other three each got a document: ISO 21448, ISO/SAE 21434, ISO/PAS 8800. The hard part is not learning four standards. It is that one item definition and one hazard list have to feed four arguments that must not contradict each other. New article on where the backbone ends.

7 min
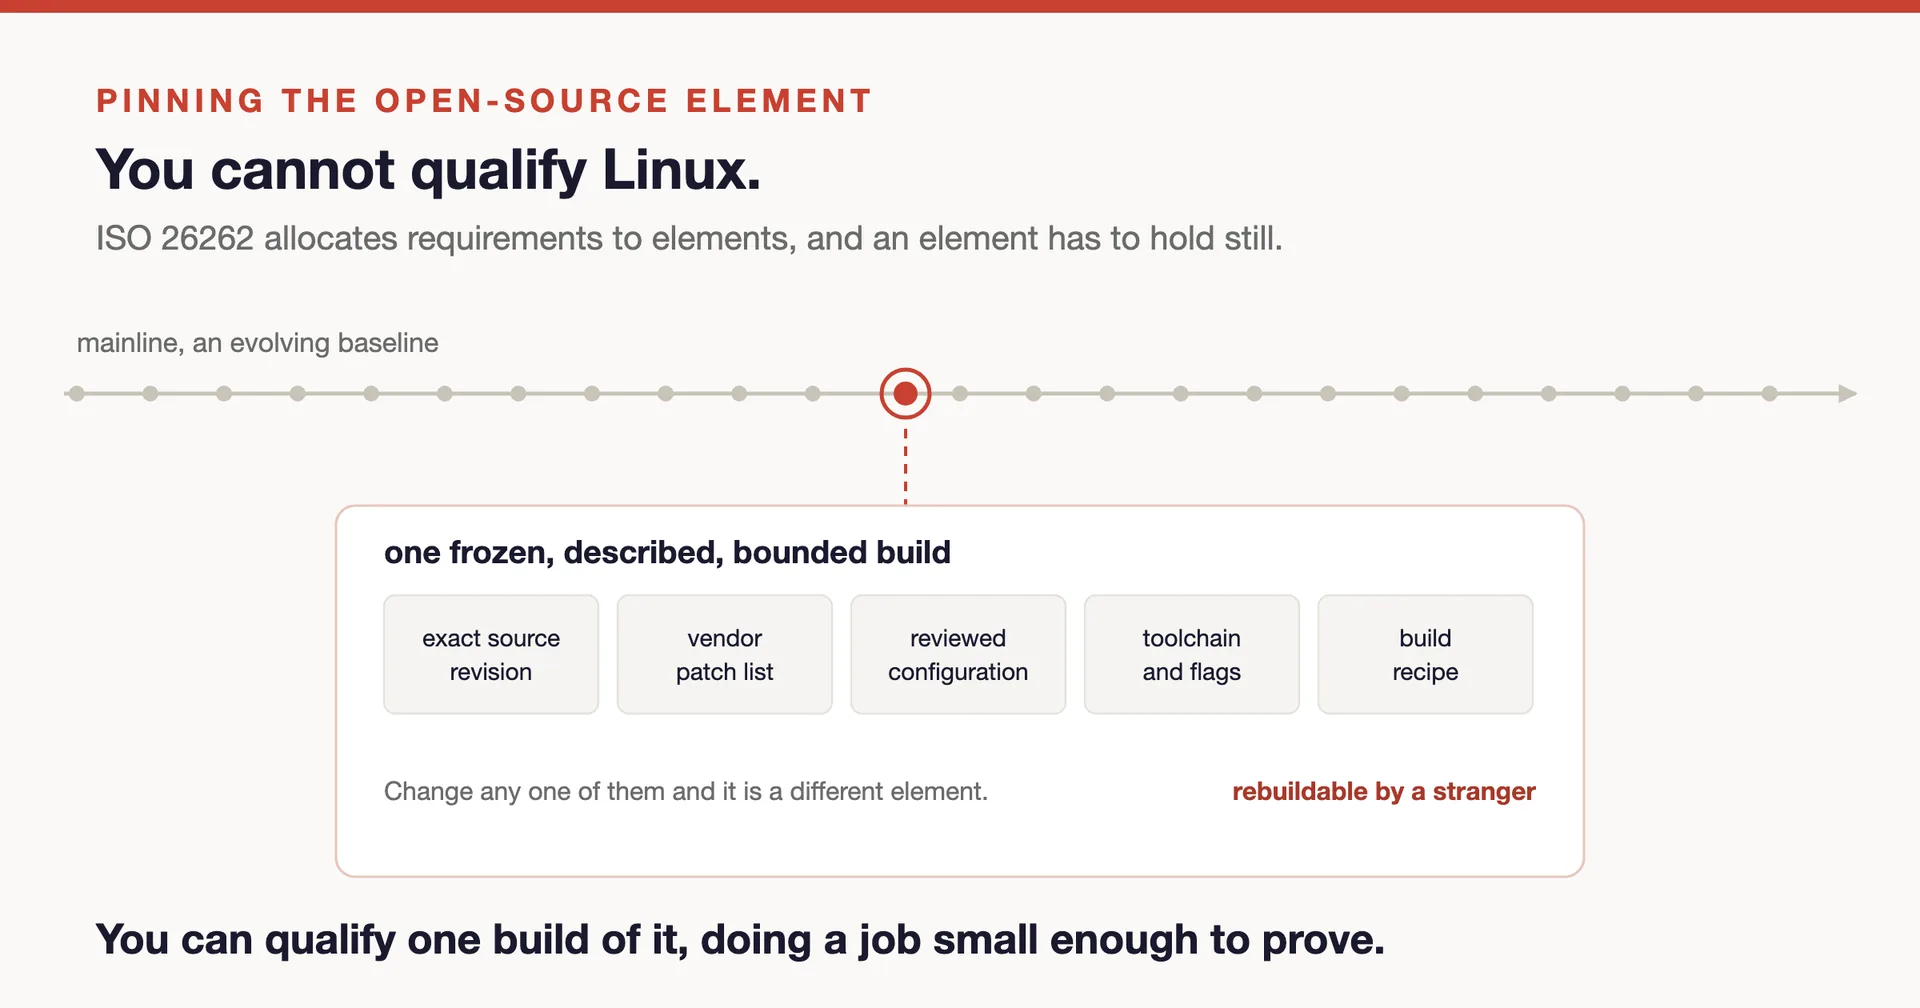
A line of commit dots labelled as the mainline runs off the right edge. One dot is ringed in red, and a dashed line drops from it into a card holding five chips: source revision, patch list, configuration, toolchain, build recipe.

Qualifying Linux for ISO 26262: Pinning the Open-Source Element

You cannot qualify Linux. You can qualify one build of it. ISO 26262 allocates requirements to elements, and an element has to hold still. A mainline kernel does the opposite. Open source gives you more visibility than any commercial supplier will. What it does not give you is traceability from a safety requirement to the test that shows it is met. So the first work product is not a gap analysis. It is a definition: exact source revision, vendor patches, reviewed configuration, toolchain, build recipe. Hand those to an engineer who was not in the room. If they cannot arrive at your binary, or explain every difference, you do not have an element. New article on the prerequisites, and why no qualification route can be chosen before the element exists.

9 min
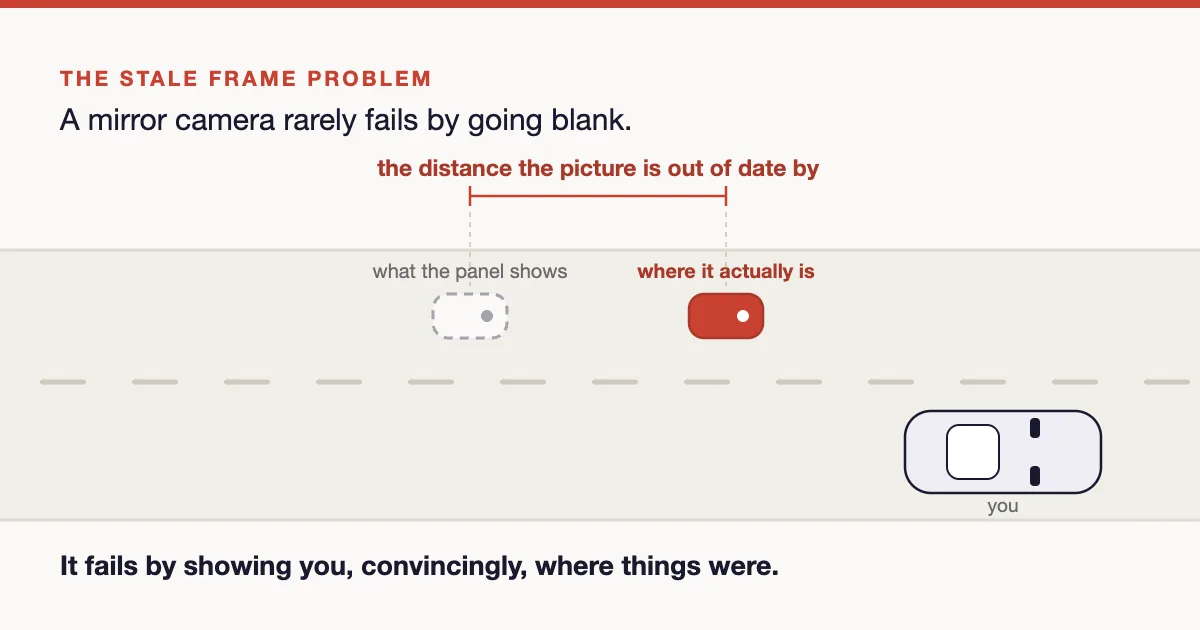
Plan view of a road. In the next lane an overtaking vehicle is drawn twice: a dashed grey outline where the mirror panel still shows it, and a solid red one further ahead where it actually is, with the gap between them marked.

Interior and Mirror Cameras: The Stale Frame Problem

A mirror-replacement camera rarely fails by going blank. It fails by showing you a well-formed picture of a road that has moved on. Most of the chain answers a different question. A link CRC proves the pixels arrived intact. A register readback proves the sensor is configured. A watchdog proves the imaging task is scheduled, and a task republishing its last buffer is scheduled perfectly. So teams add a frame counter, usually in the software that receives frames. That proves only that this software is running: it keeps counting while the sensor sits dark. Even minted at the sensor, a counter is metadata: it travels next to the pixels, not inside them. A stage that re-stamps on publication can attach a fresh number to old pixels, and a header-only check waves it through. Placement earns you sequence coverage. Claiming the picture is current is a bigger claim than most safety cases support. New article on what that costs in detection budget and where the ISO 21448 boundary falls.

8 min
Car bodies on a factory assembly line, a dark hatchback with its doors and bonnet open in the foreground and a row of white and blue bodies receding down the line behind it, under overhead conveyor gantries.

ASPICE and ISO 26262: What Each One Actually Grades

ASPICE rates how capable your development process is. ISO 26262 asks whether the product it produced is acceptably safe. Neither verdict substitutes for the other. Where the two read the same artifacts, where they diverge, and the safety work that has no ASPICE process behind it.

7 min
Close-up of a densely populated circuit board, with a square multi-pin integrated circuit in sharp focus among capacitors and smaller packages.

Multi-Core Safety Architectures: An ISO 26262 Overview

Multi-core automotive SoCs add shared hardware, mixed criticality, and timing interference to every safety argument. This article maps the families of multi-core safety architecture, the three interference concerns underneath them, and what actually decides which one fits.

6 min
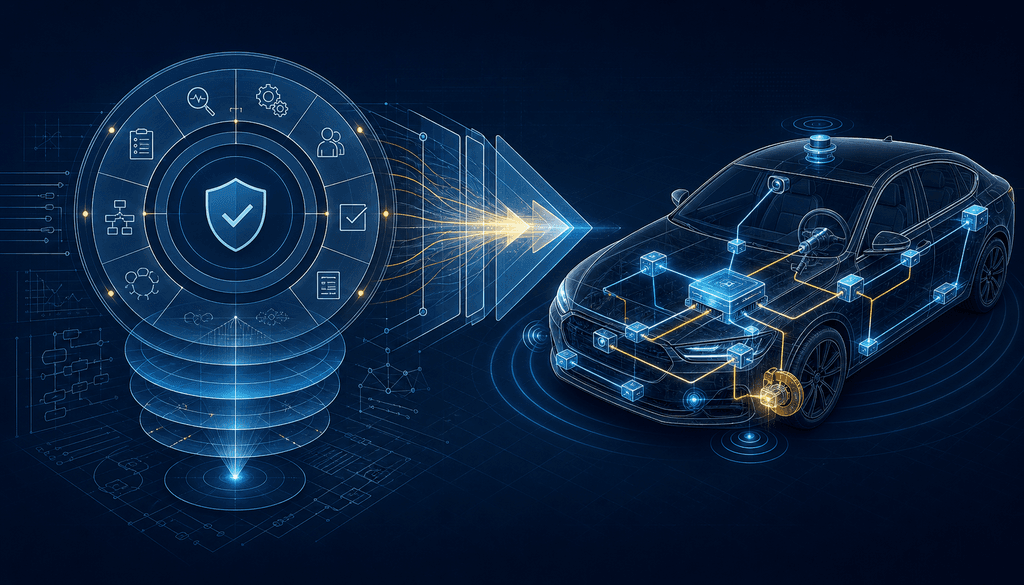
Technical illustration showing a generic functional-safety lifecycle being adapted into the electronic architecture of a modern road vehicle.

IEC 61508 vs ISO 26262: What Automotive Engineers Need to Know

Can an element assessed at IEC 61508 SIL 3 support an ISO 26262 ASIL D safety goal? Often yes, but the label proves nothing on its own: a SIL belongs to a safety function, not to a part. Why the two risk models look alike and still cannot be converted, and what an integrity level is attached to.

9 min
A comparison table showing the differences between automotive functional safety standard ISO 26262 and machinery standards ISO 13849 and IEC 62061.

Automotive vs Machinery Functional Safety: An ISO 26262 Comparison

While automotive and machinery functional safety share common roots, their methodologies differ significantly. Explore how ISO 26262 compares to ISO 13849 and IEC 62061 in risk assessment and system architecture.

8 min
Comparison table showing aerospace functional safety standards like DO-178C and ARP4754A next to their automotive ISO 26262 equivalents for system, software, and hardware development.

Functional Safety in Aerospace vs Automotive: An ISO 26262 Guide

Discover how aerospace functional safety standards like DO-178C and ARP4754A compare to automotive ISO 26262. Learn what automotive engineers can adapt from aviation to build robust, fail-operational architectures for autonomous vehicles.

7 min
A digital automotive instrument cluster displaying a steering failure warning, illustrating HMI safety mechanisms and ISO 26262 compliance for vehicle displays.

Mastering HMI Display Safety for Automotive ISO 26262

Automotive display systems are the final line of defense during vehicle failures. Learn how to engineer robust HMI warning strategies, manage arbitration chaos, and calculate strict timing budgets to achieve ISO 26262 compliance.

7 min