Dependent Failure Analysis: Three Checks Beyond Redundancy
Two channels can still share one vulnerability. Learn three practical DFA checks for examining common causes, hidden dependencies and the evidence behind independence claims.
3 min
36 articles
Two channels can still share one vulnerability. Learn three practical DFA checks for examining common causes, hidden dependencies and the evidence behind independence claims.
Hardware can fail systematically, through errors made during development, or randomly, as parts wear or break in service. FMEDA addresses the random failures, connecting failure analysis with stronger evidence and better engineering decisions. Explore five reasons it matters for ISO 26262 projects, from revealing diagnostic gaps and examining supplier assumptions to guiding improvements and keeping the safety argument aligned with a changing design.
 Miscellaneous
Years on the road do not automatically make a component proven in use. What makes field history credible under ISO 26262, and when can it support reuse? A practical introduction to the evidence, limits and common misconceptions.
 Miscellaneous
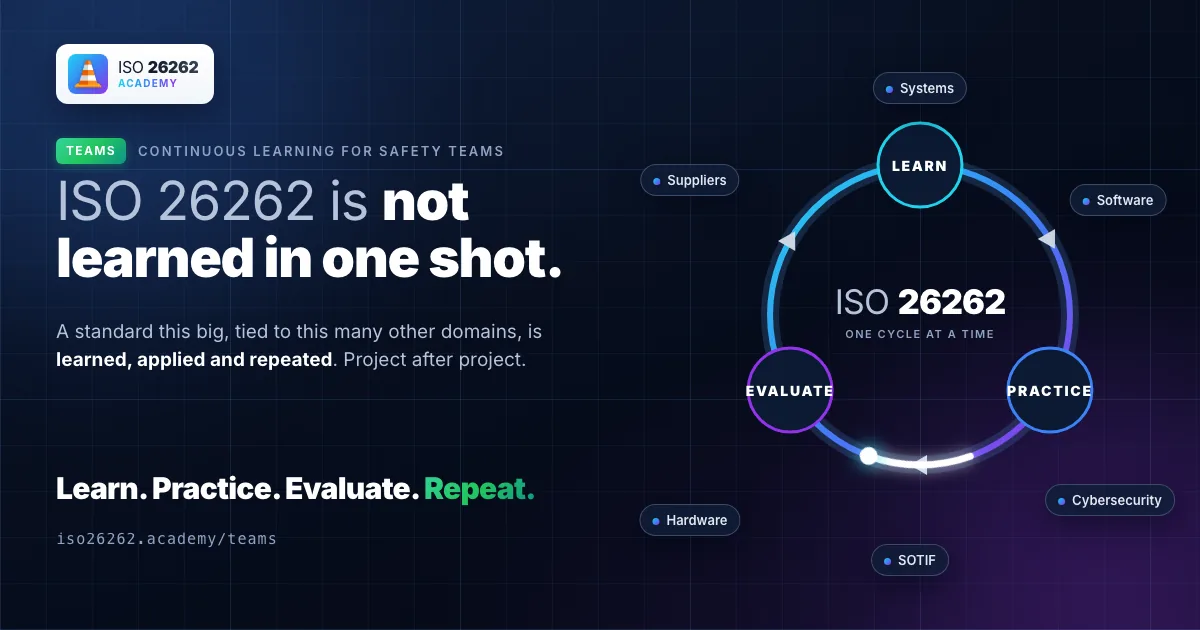
A training week, a certificate, and six months later a blank hazard analysis template. Nothing went wrong with the course. ISO 26262 is used in slices, months apart, and every slice borrows knowledge the standard does not teach: vehicle dynamics, reliability data, software verification, supplier contracts, SOTIF, cybersecurity. It is not learned in one shot. It is learned, applied and repeated, one cycle at a time. New article on how a team keeps that loop running, and what evidence it leaves behind.
 Technical
ASPICE rates how capable your development process is. ISO 26262 asks whether the product it produced is acceptably safe. Neither verdict substitutes for the other. Where the two read the same artifacts, where they diverge, and the safety work that has no ASPICE process behind it.
 Technical
Multi-core automotive SoCs add shared hardware, mixed criticality, and timing interference to every safety argument. This article maps the families of multi-core safety architecture, the three interference concerns underneath them, and what actually decides which one fits.
 Technical
Can an element assessed at IEC 61508 SIL 3 support an ISO 26262 ASIL D safety goal? Often yes, but the label proves nothing on its own: a SIL belongs to a safety function, not to a part. Why the two risk models look alike and still cannot be converted, and what an integrity level is attached to.
 Miscellaneous
While both automotive and railway safety standards originate from IEC 61508, they have evolved into distinct methodologies. Discover how ISO 26262 principles compare to CENELEC railway standards regarding risk assessment, system response, and lifecycle management.
 Technical
While automotive and machinery functional safety share common roots, their methodologies differ significantly. Explore how ISO 26262 compares to ISO 13849 and IEC 62061 in risk assessment and system architecture.
 Technical
Discover how aerospace functional safety standards like DO-178C and ARP4754A compare to automotive ISO 26262. Learn what automotive engineers can adapt from aviation to build robust, fail-operational architectures for autonomous vehicles.
 Technical
Automotive display systems are the final line of defense during vehicle failures. Learn how to engineer robust HMI warning strategies, manage arbitration chaos, and calculate strict timing budgets to achieve ISO 26262 compliance.
 Technical
Discover how to accelerate automotive software engineering using Model-Based Development. This guide covers essential ISO 26262 Part 6 requirements, from enforcing strict modeling guidelines to performing Model-in-the-Loop testing and automatic code generation.
Keep learning
Each guide is a full course with diagrams and worked examples. Open one to see what it covers.